

/admin/audit.
Administrators and auditors. It is the one page in the admin area with a wider audience: an
auditor reaches this and nothing beside it, which is what lets somebody read the trail without
being able to act on the platform.
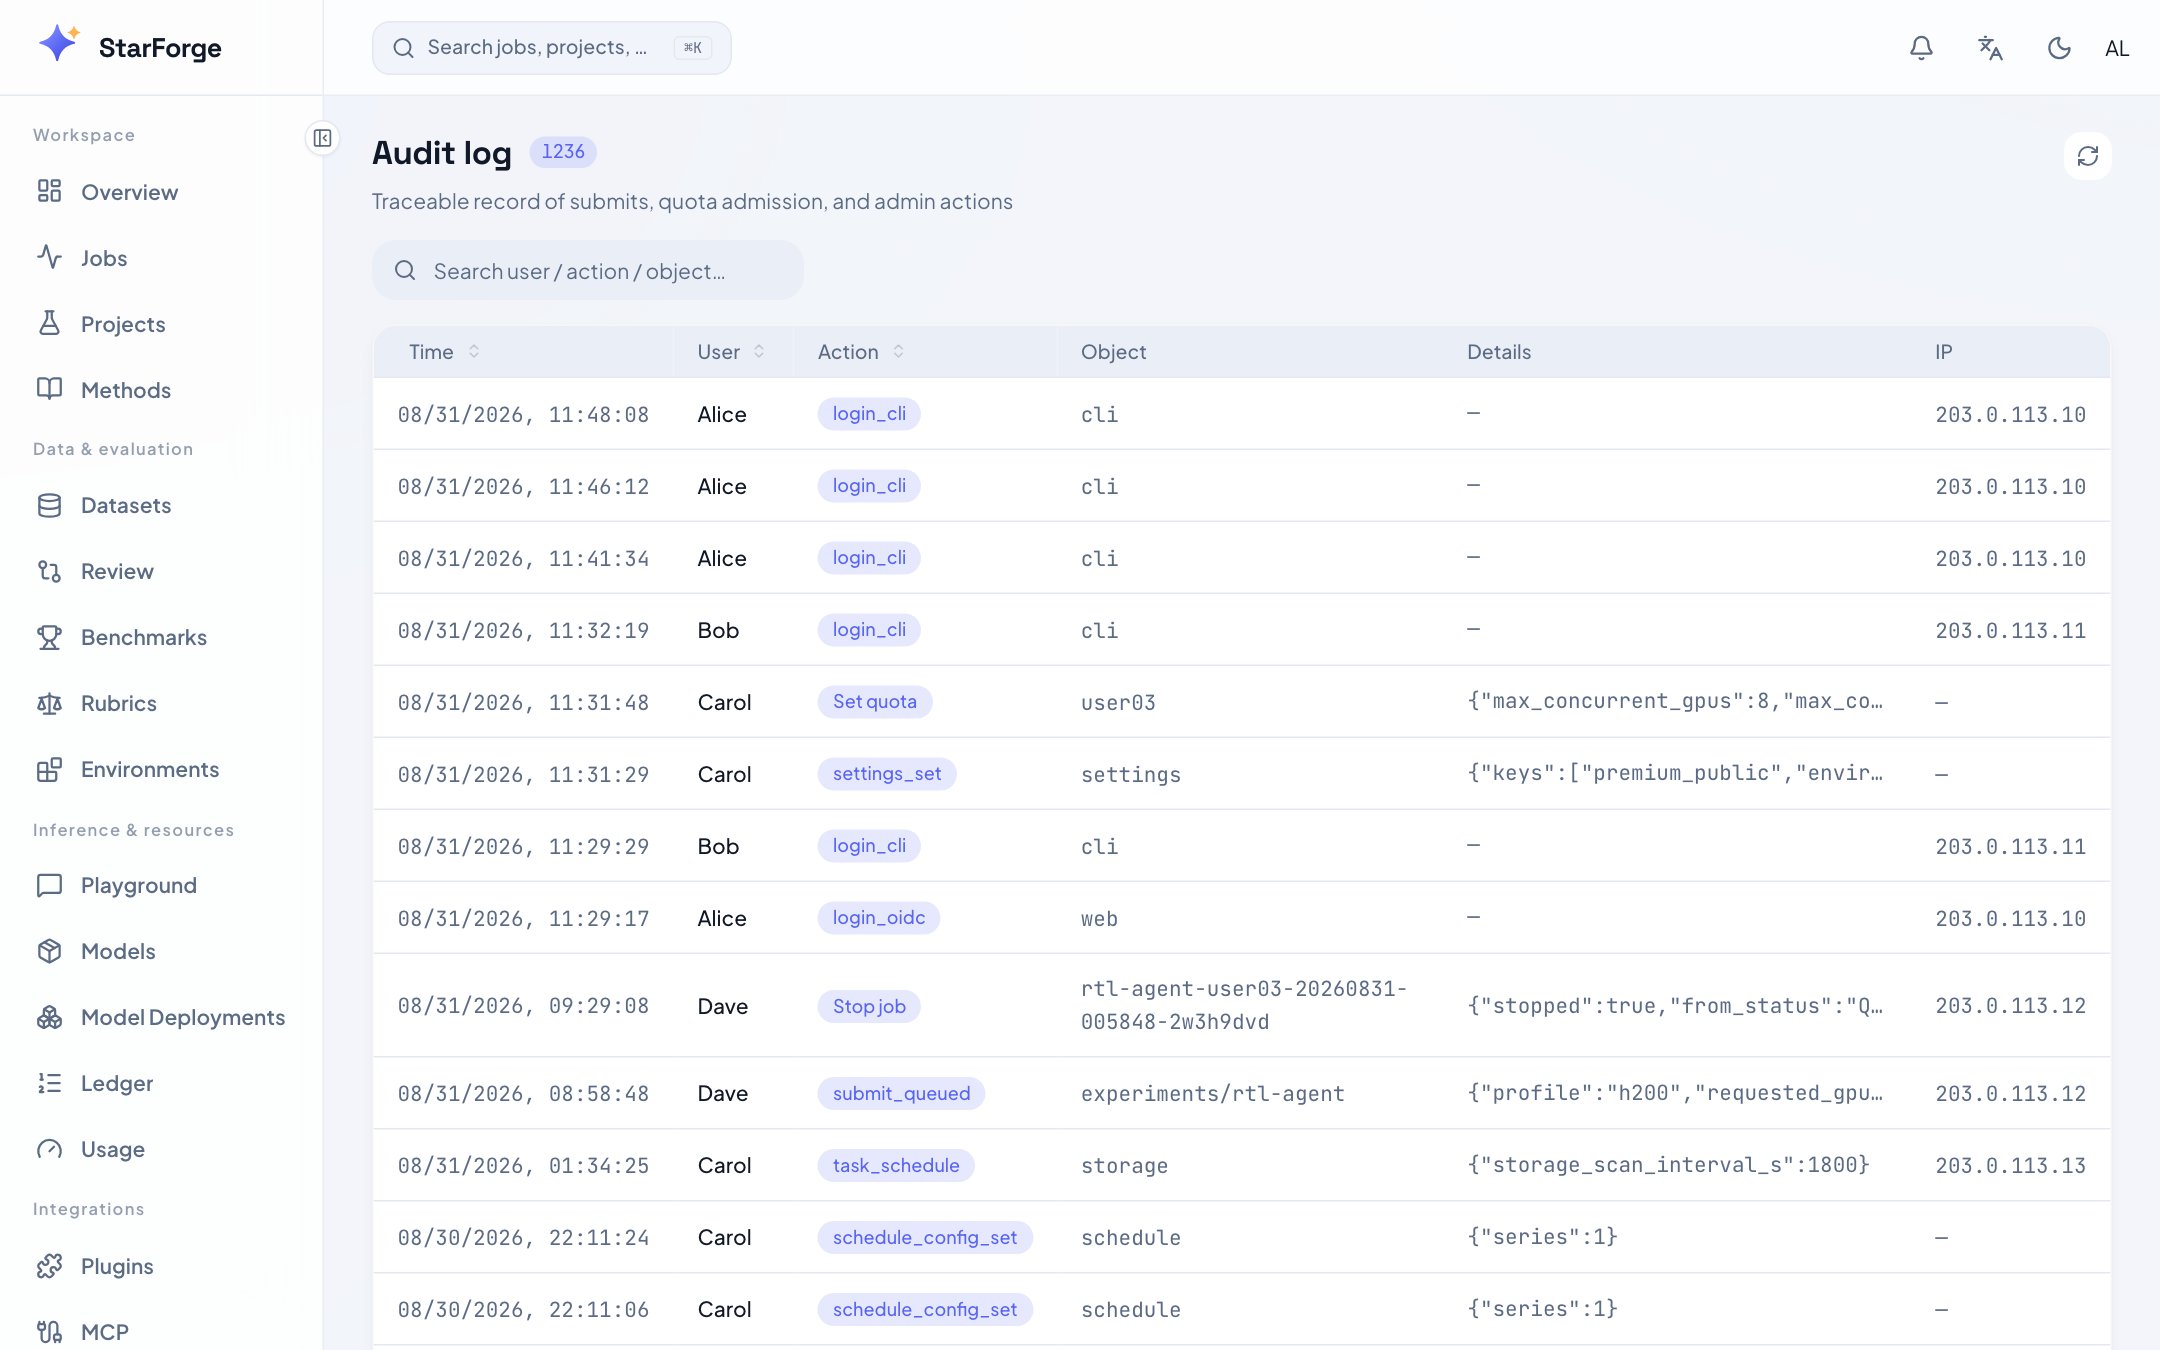
The audit log: user, action, object and source address.
What is recorded
Each entry carries the user, the action, the object and the time. Search matches across user, action
and object.
What it is for
Two questions, in practice. “Why did my job not run?” — a refusal at admission is recorded with the gate that refused it, so the answer survives past the moment the error message scrolled away. “Who stopped my run?” — stops, deletions and bulk cleanups are attributed. On a shared cluster this is what keeps an operational action from becoming an accusation.The trail records control-plane actions, not training content. It will tell you that somebody
submitted a job and what its id was; it will not tell you what was in the data.